Syslog server for Windows
Syslog Watcher
The actively developed Windows syslog server. Collect, store, analyze, alert, and forward system messages from every device on your network — in one place.
23,000+ licenses sold in 89 countries. Set up in five minutes. Keep the log history that PCI DSS, HIPAA, and SOX audits ask for.
- High-performance multithreaded architecture
- Virtual and cloud environment compatible
- Collect, forward, analyze, and export syslog messages
- Flexible syslog parser and comprehensive filter rules
- Alert expressions and syslog reports
- SIEM integration and filtered forwarding
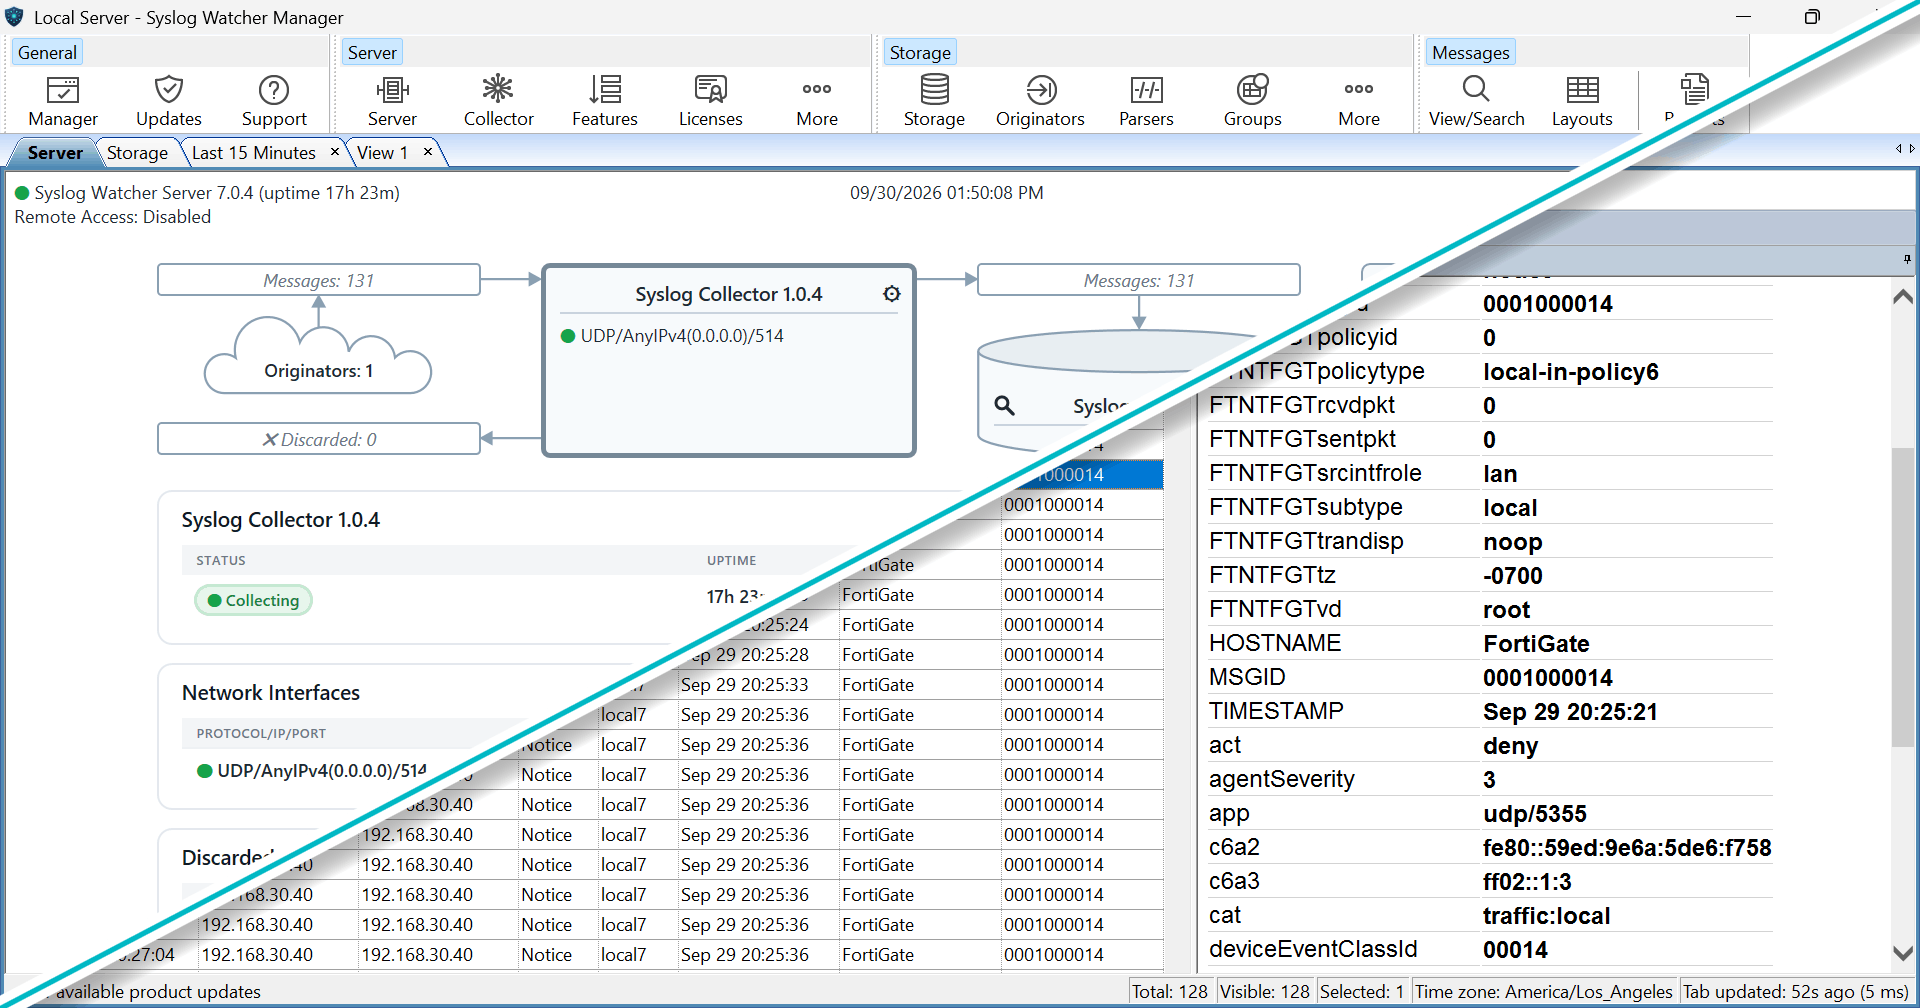
What is Syslog Watcher?
Windows does not ship with a built-in syslog server. Syslog Watcher fills that gap — the syslog for Windows solution network teams use when they need native collection on Windows Server and desktop editions. How to install a syslog server on Windows Server, or browse resources.
Capabilities
End-to-end syslog management
Four parts of Syslog Watcher work together to turn raw network chatter into something you can search, keep, and forward.
- CollectUDP, reliable TCP, and encrypted TLS — accept syslog from any network device.
- StoreSQLite-backed engine wrote 35k+ msg/s in our tests, with built-in retention.
- AnalyzeFilters, a virtualized viewer, and instant search across millions of messages.
- ForwardForward to SIEM over UDP/TCP/TLS, or export to ODBC, CSV, XML, and JSON.
Compatibility
Works with everything you already run
If it speaks syslog, Syslog Watcher receives it.
Network gear
Cisco · Fortinet · Palo Alto · SonicWall · Meraki · Ubiquiti · MikroTik · Sophos · Juniper · Aruba · Extreme
Servers & endpoints
Linux syslog/journald · Windows Event Log (via EventLog Inspector) · ESXi · VMware vCenter · Proxmox · TrueNAS · Synology · QNAP
Forwards to
Splunk · Graylog · QRadar · Microsoft Sentinel, Datadog, Sumo Logic, Elastic (via their syslog collector) · Generic UDP / TCP / TLS
Runs on
Windows 8.1, 10, 11 · Windows Server 2012 R2, 2016, 2019, 2022, 2025 · Bare-metal, VM, or cloud Windows instance
19
Years of experience
since Syslog Watcher 1.0 (May 2007)
23k+
Licenses sold
to customers who prefer Syslog Watcher
24
Resellers
distribute Syslog Watcher worldwide
89
Countries
with Syslog Watcher customers
Testimonials
What customers say
From administrators who collect syslog on Windows.
“The new Syslog Watcher 7 release looks really good so far! We’ve started looking at the new version and are very positive about the improvements. Thanks, and keep up the good work with version 7!”
Business customer, Sweden
“I have gone ahead and fresh installed v7. A big leap indeed, and from what I can initially tell, the leap produced a well organized intelligent system of log message collection, management, and reporting.”
Rob C., Verified User
“We have found Syslog Watcher 6.5.17 and 7.0.5 to be brilliant pieces of syslog software. To me, they are probably the best made. Please keep up the solid work”
IP PBX Support
Why teams pick it
Built for the work you actually do
01
Syslog Server for Security
Network devices log failed logins, blocked connections, and configuration changes. Collected in one place, those messages show suspicious activity while it is happening, so an administrator can respond before it spreads.
Syslog Watcher alerts on the messages you mark as suspicious, so a brute-force attempt or an unexpected admin login reaches someone’s inbox instead of waiting in a device’s log buffer.
Alerts fire on a matching message as it arrives — not at the next manual log review.
02
Syslog Server for Compliance
PCI DSS (Requirement 10) and HIPAA (§164.312(b)) require audit logs of activity on the systems they cover. SOX controls, GDPR, and CCPA ask for appropriate security, and retained logs are a common way to show it. A syslog server keeps that record in one place, away from the devices that produced it, and you can copy the archive to cloud storage for longer retention.
Syslog Watcher collects over TLS (RFC 5425) and keeps a compressed archive of the collected messages, synced daily and optionally encrypted with a password. You set how many days the storage and the archive keep messages.
- PCI DSS
- HIPAA
- SOX
- GDPR
- CCPA
03
Troubleshooting with Syslog Server
Syslog servers are commonly utilized to troubleshoot network issues. When a network device or server is not operating correctly, the syslog server can provide valuable information about what went wrong and when.
Syslog Watcher filters and searches messages from every device at once, so you can go from “the VPN dropped at 3 a.m.” to the message that explains it without logging in to each device.
04
Network Visibility & Proactive Management
With a syslog server, organizations gain greater visibility and control across their infrastructure to address critical challenges such as optimizing system performance. Without a centralized message server, important log data can be scattered across different devices, making it difficult to correlate.
By analyzing log data, you can gain insights into network usage patterns, identify potential bottlenecks, and plan for future capacity upgrades.
05
Integration with SIEM Solutions
Syslog Watcher integrates with other troubleshooting and monitoring tools, such as SIEM systems, network monitoring solutions, and database servers.
SIEM systems use advanced analytics, machine learning, and correlation rules to detect potential security threats and anomalies. By feeding them via Syslog Watcher, the SIEM gets richer log data and improves its ability to identify suspicious patterns.
Customers
Used by teams at organizations including
All logos, trademarks, and registered trademarks are the property of their respective owners.
FAQ
Common questions
Free License, evaluation, Windows syslog server, and how Syslog Watcher fits a SIEM or compliance archive.
Does Windows include a syslog server?
Is there a free license?
What do I get during the 30-day evaluation?
Is it a one-time purchase or a subscription?
How do I count syslog originators for license sizing?
What Windows versions are supported?
Which syslog standards and protocols are supported?
Can I forward to my SIEM — Splunk, Sentinel, Elastic, Graylog, QRadar, Datadog?
Does it help with PCI DSS, HIPAA, SOX or GDPR compliance?
How fast is the storage and how much data can it hold?
How long does installation take?
Where is my data stored, and how do I get support?
Try Syslog Watcher today
The installer includes a Free License by default (3 syslog originators). You can request any license type for a 30-day evaluation for free, so you can verify everything on your own infrastructure.